-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Omar Cruz
Chief Information Security Officer
Balancing Innovation, Risk and Business Priorities in Modern Cybersecurity
Omar Cruz, Chief Information Security Officer, Bluerity
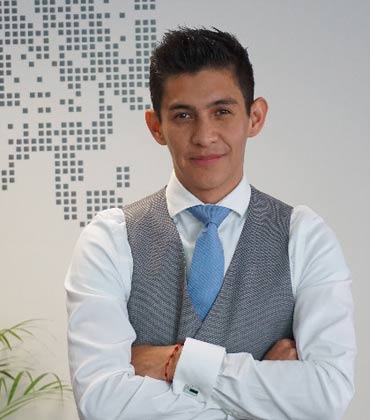
Omar Cruz brings more than 12 years of cybersecurity experience across Latin America and Europe, with expertise in cybersecurity strategy, risk management, governance and security transformation. Throughout his career, he has helped organizations strengthen their security maturity while aligning cybersecurity initiatives with business objectives.
Currently serving as Chief Information Security Officer at Bluerity, Cruz leads strategic initiatives that integrate security with operational performance and business objectives. As a member of the board of directors, he advocates for cybersecurity as a strategic investment, while championing greater security awareness across organizations and individuals alike.
Balancing Regional Realities with Global Security Standards
I believe in fostering a culture of objectivity and continuous improvement, where standards serve as a foundation for excellence rather than a compliance burden. This mindset extends across our organization and is shared with both our clients and employees.
Latin America presents a unique set of regulatory, economic and cybersecurity challenges. To address these effectively, I focus on creating a balance between immediate threats and the inherent risks associated with each organization's operations. Building a sustainable security strategy requires maximizing operational, technological and financial resources while ensuring they are aligned with business objectives.
While there is no shortage of security solutions available today, effective cybersecurity is not achieved through technology acquisition alone. It begins with a thorough assessment of the impact scenarios an organization may face and the level of risk it is prepared to accept.
We promote a proactive approach to security. We recognize that cybersecurity is built incrementally through the actions of every employee, every day. It is not solely the responsibility of the technologies deployed within an organization but a shared commitment embedded throughout the business.
Aligning Security Investments with Business Priorities
In my view, the most effective way to navigate budget constraints is to begin by understanding business priorities and evaluating them alongside the solutions available in the market.
Established global vendors often provide confidence and proven capabilities. However, I also believe it is important to assess emerging providers in both local and international markets. Many of these companies offer innovative, high-quality solutions that may not address every stage of the threat management lifecycle but can effectively strengthen critical areas of an organization's security posture.
By combining established solutions with emerging alternatives, organizations can manage budget limitations more effectively while directing resources toward initiatives that support executive objectives. This approach allows security leaders to drive meaningful improvements, even when certain initiatives fall outside traditional spending priorities or annual cybersecurity budget allocations.
 The most effective leaders are those who can respond to challenges with agility while remaining receptive to new ideas and approaches.

Preparing for the Next Wave of Cybersecurity Challenges
Among the most significant developments security leaders must address today are cloud migration and the integration of artificial intelligence into business operations.
As organizations accelerate cloud adoption, many implement new technologies and services without fully understanding the security controls and governance frameworks required to protect them effectively. This creates potential exposure that may not become visible until much later.
Artificial intelligence presents a similar challenge, particularly when deployed in environments that process sensitive information or support critical business functions. While AI offers significant opportunities, its implementation must be accompanied by a clear understanding of associated risks, governance requirements and security implications.
Both cloud transformation and AI adoption are areas where organizations can underestimate risk, either because of limited knowledge or because technological innovation often advances faster than organizational readiness. For this reason, I believe these initiatives should be carefully planned and guided by experienced professionals who possess practical expertise in implementing and securing these environments.
Advice for the Next Generation of Security Leaders
My advice to aspiring CISOs and security executives is simple: never stop learning.
The world continues to evolve rapidly, both technologically and socially, making continuous education essential. Whether through industry experts, conferences, books, research publications, daily briefings, or professional networks, security leaders must maintain a constant commitment to expanding their knowledge and perspective.
Equally important is cultivating an open mindset and the ability to adapt to changing circumstances. The most effective leaders are those who can respond to challenges with agility while remaining receptive to new ideas and approaches.
While technical expertise remains a fundamental requirement, long-term success in cybersecurity leadership depends on more than technical knowledge alone. Future CISOs must be able to translate complex security concepts into clear business language, helping stakeholders understand both the risks they face and the value security brings. The ability to connect cybersecurity outcomes with real-world benefits is what enables leaders to build trust, influence decision-making and create lasting impact across both professional and personal environments.
Bluerity
Chief Information Security Officer
Omar Cruz brings more than 12 years of cybersecurity experience across Latin America and Europe, with expertise in cybersecurity strategy, risk management, governance and security transformation. Throughout his career, he has helped organizations strengthen their security maturity while aligning cybersecurity initiatives with business objectives.

