-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Céu Frank Serikawa Balzano
Founder and CISO
Redefining Security Awareness in Latin America
Céu Frank Serikawa Balzano, Founder and CISO, CULTSEC and CISO (as a service), Zatlas
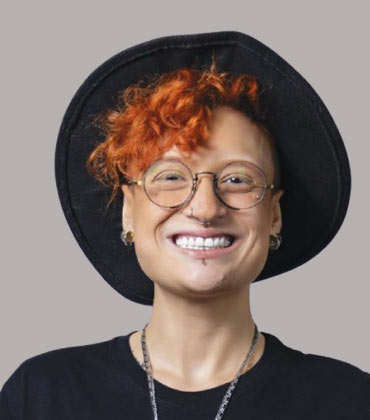
Céu Frank Serikawa Balzano is a cybersecurity governance and GRC leader known for his work in security culture, compliance and human risk management across Latin America. As founder of CULTSEC and CISO-as-a-Service at Zatlas, he helps organizations strengthen cybersecurity maturity through governance strategy, executive engagement, awareness initiatives and risk-focused security programs, including an ROI-driven awareness program that connects investment in security culture to concrete business outcomes.
His experience includes frameworks such as ISO 27001, SOC 2, LGPD, GDPR, NIST and PCI DSS, alongside work involving audits, security policies, access management and executive reporting across governance, compliance and operational security environments. He also organized one of Latin America’s early cybersecurity awareness events, supported by the SANS Institute.
Embedding Human Risk into Daily Security Culture
I help organizations move beyond compliance-driven security and bring risk management into the daily operational routine of the business. Security cannot exist only as an audit requirement. It needs to connect with real operational workflows, including access management and incident response.
A major part of this process is human risk. Companies invest heavily in EDR, XDR and firewalls, but many incidents still start with human behavior. A single phishing click can expose the entire organization. And that cost is not abstract. According to IBM’s 2025 Cost of a Data Breach report, the average breach in Brazil reaches R$7.19 million, a figure that shows up as operational downtime, LGPD penalties and reputational damage. That is why security awareness cannot be treated as just a once-a-year training exercise. It needs to be an information security control as important as an EDR or a firewall, and it requires looking at how people actually behave, not how they should. People reuse passwords, click in a hurry and work around controls, and it is that real behavior that defines the risk surface.
This is also why executive and board alignment are so important. It falls to leadership, not only to the cybersecurity team, to understand the business impact of human risk and governance gaps. For those who live security day to day, this is obvious, but many senior executives still see awareness as a cost with no return. It was to address that skepticism that I developed an ROI-driven awareness program that translates the investment into metrics the board understands.
Breaking down Compliance Silos
When companies start dealing with frameworks like ISO 27001, SOC 2, LGPD, GDPR or PCI DSS, the biggest mistake is treating each one as a separate project owned only by cybersecurity. These requirements affect legal teams, compliance, vendors, contracts, operations and leadership, so security needs to work across the entire company. I usually start by identifying the controls that overlap across frameworks and building a centralized governance structure that can support multiple requirements simultaneously. I also separate what is mandatory for the business, such as LGPD, GDPR, PCI DSS and BACEN, from what is connected to business maturity and customer trust.
Even so, there is a limit that no framework reaches on its own. Improper use of devices, unsecured home Wi-Fi while working remotely, or QR codes scanned on devices connected to the company network are rarely covered by an audit. That is why a mature security culture requires a human lens, one that goes beyond compliance and takes into account how people behave and the particularities of each business.
From Annual Training to Human-Centered Resilience
When I began working with security awareness in Brazil, the maturity level was still very low. Most companies only did annual mandatory training, especially in the banking sector, and that was considered enough. The country did not yet have LGPD or the ANPD, and security awareness was still treated mostly as a compliance obligation. The turning point came with WannaCry in 2017. There was the technological problem and the patch issue, but the trigger was human behavior, and companies began viewing security awareness very differently.
In the beginning, most initiatives focused on basic training and phishing simulations. Today, the approach is much more mature, with executive training, social engineering simulations, gamified experiences, videos, escape rooms and continuous campaigns. Security culture is no longer only an IT responsibility. One central challenge is dealing with generational diversity. The same environment brings together everyone from baby boomers to Generation Z, and each one learns in a different way and stumbles into different risks. Treating everyone with the same format does not work, and awareness needs to speak to each profile. That is also the philosophy behind CULTSEC, focused on building a long-term security culture that becomes part of the organization’s daily operations.
Security culture is no longer only an IT responsibility. It needs to involve everyone, from operational teams to leadership and the board.
Transforming Security Culture in Brazil
Throughout my journey, my proudest accomplishments involve governance maturity and security culture transformation. Achieving certifications like SOC 2 Type II and ISO 27001 was extremely challenging because they require strong operational processes and continuous improvement, and they helped strengthen risk management and resilience inside the companies I worked with.
At the same time, one accomplishment that is especially meaningful to me is having helped advance cybersecurity awareness in Brazil. Having organized one of Latin America’s early cybersecurity awareness events, supported by the SANS Institute, helped contribute to the evolution of cybersecurity awareness maturity in the country, at a time when most organizations still treated awareness primarily as a compliance obligation.
Over the years, I’ve worked to move beyond isolated training and build more continuous, human-centered programs. Founding CULTSEC was an important milestone because it allowed me to focus on strengthening security culture and long-term resilience. Looking ahead, I believe the next step in maturity in Brazil is to stop measuring awareness by the number of trainings and start measuring it by the behavior it changes. It only fulfills its role when it is continuous, aligned with the company’s culture, when it speaks to the reality of each employee and demonstrates value through clear metrics, including return on investment. As long as security is seen only as a technical area, and not as part of the culture and the strategy, there will always be a gap to fill. That is exactly where I intend to keep contributing.
Zatlas
Founder and CISO
Céu Frank Serikawa Balzano is a cybersecurity governance and GRC leader known for his work in security culture, compliance and human risk management across Latin America.

