-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- AUGMENTED & VIRTUAL REALITY
- COLLABORATION
- CONVERSATIONAL
- CUSTOMER EXPERIENCE MANAGEMENT
- CUSTOMER RELATIONSHIP MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DIGITAL CUSTOMER EXPERIENCE
- DOCUMENT MANAGEMENT
- EHS SOFTWARE
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE DATA QUALITY MONITORING
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- GAMIFICATION
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Contributory Virtus Investment Partners on the invitation from our Editorial

BRAVA Energia
Henrique Kronemberger, IT & Cybersecurity ManagerCybersecurity That Works Where It Matters Most
Henrique Kronemberger, IT & Cybersecurity Manager
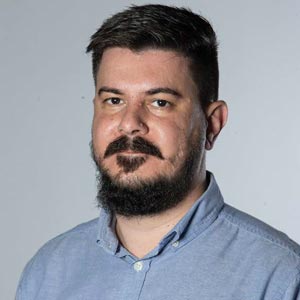
Henrique Kronemberger is an experienced IT and Cybersecurity Manager with a strong technical background shaped by hands-on work across Upstream, Midstream, and Downstream operations. His close involvement in the field has given him a practical understanding of the challenges faced by engineers and operations teams, enabling him to communicate and implement cybersecurity strategies that truly resonate with frontline stakeholders.
Modernizing Legacy Systems in High-Risk Environments
From the very first asset transition at the company, I have been part of our ongoing efforts to revitalize legacy environments. We have implemented secure connectivity strategies, introduced network segmentation, and adopted modern monitoring technologies—always respecting the operational and budgetary constraints of each asset.
One of the most complex projects I worked on was the integration of the Potiguar Cluster, where midstream and downstream processes added complexity due to the facility size and numerous legacy systems. This experience emphasized the importance of maintaining an up-to-date asset inventory and having a deep understanding of the operational environment to design realistic, scalable IT/OT integration strategies.
In high-risk industrial environments, cybersecurity must align with core business priorities. My approach focuses on tailored, cost-effective solutions—often developed internally—that ensure operational continuity while meeting technical requirements and industry best practices.
Aligning Cyber Strategy with Business Objectives
Ensuring that the technical strategy aligns with business objectives starts with understanding the operational context and speaking the language of the business. In oil and gas, projects must support reliability, regulatory compliance, and production continuity. I begin every initiative—data inventory, disaster recovery, or global security architecture—with a risk-based assessment that maps technical outcomes to business impact and informs confident decisions.
Each asset may require a tailored solution based on its maturity and operating conditions; yet, every design aligns with our global cybersecurity architecture, which is grounded in the NIST Cybersecurity Framework (CSF). This ensures a consistent risk posture, visibility, and governance enterprise-wide, even when implementations differ.
In legacy environments, we may vary backup methods or monitoring tools, but all adhere to common controls, including asset identification, detection capabilities, response playbooks, and recovery standards. This harmonized approach supports regulatory requirements, improves audit readiness, and protects productivity.
I also use the NIST CSF to link technical planning with governance, reporting cybersecurity performance alongside core business KPIs in leadership discussions.
 In high-stakes environments like the oil and gas industry, where cybersecurity incidents can impact safety and production, my approach is always business-driven

Ultimately, alignment depends on striking a balance between flexibility and standardization. When this balance is achieved, IT and cybersecurity solutions remain context-specific yet globally coherent, enabling the business to reinforce confidence in its security posture over time across all assets.
Leading Incident Response with Clarity and Focus
In high-stakes environments like the oil and gas industry, where cybersecurity incidents can impact safety and production, my approach is always business-driven. This approach is not just about technical solutions, but about understanding the business and its critical operations. I focus first on protecting these critical operations and minimizing any disruption to the core business. This means quickly assessing which systems are essential to uptime and prioritizing response actions accordingly.
What made the difference was our ability to stay focused on business impact, not just technical details. Under pressure, teams remain calm when they understand the business rationale behind every move. That’s why I lead with clarity, not blame—ensuring that everyone understands the mission: protect operations, preserve evidence, and restore services safely. This commitment to safety reassures stakeholders of our priorities.
Balancing Innovation, Connectivity and Cyber Risk
It requires a deep understanding of how innovation can affect operational risk. I take a pragmatic, business-aligned approach: every new technology or integration is assessed not only for its technical benefits, but also for its impact on safety, continuity, and cost efficiency.
We often employ remote access, AI-based penetration testing, and cloud-based reporting. These innovations support operational efficiency, but they also introduce new risks. My role is to ensure that security is embedded early, not bolted on later through risk assessments, secure architectures, and controls adapted to the asset’s maturity.
At the same time, I steer clear of a one-size-fits-all approach. Security that is too rigid can stifle innovation and impede production goals. Instead, I work closely with engineering and operations teams to design controls that are effective and realistic, tailored to the specific needs of the organization and balancing exposure, compliance needs, and business value.
Ultimately, it’s about enabling innovation safely, with cybersecurity as a strategic partner, not a barrier to transformation.
Ground-Up Cyber Leadership in Industrial Settings
My first piece of advice: immerse yourself in the environment and observe the daily operational processes up close. Before implementing controls, policies, or frameworks, you need to understand how the business truly works on the ground. If your strategy is built from the office, detached from real operational conditions, it may look good on paper, but it won’t survive the field.
Why? Since operations teams are focused on delivering results, if your cybersecurity plan becomes a barrier to that, with dozens of rules that disrupt continuity, it will be seen as an obstacle, not a partner.
Start by visiting each facility. Map the assets yourself. Talk to the people who’ve been working there the longest, whether they’re in your organization or former employees you can reach. They hold critical knowledge about the behavior and quirks of each asset, which is invaluable for designing practical, risk-informed solutions.
And here’s something many leaders learn the hard way: even with full executive sponsorship, when your cybersecurity roadmap is placed on the table alongside operational results, the latter will almost always take priority. That’s not a failure of leadership, it’s a reality of the industrial sector. Understanding and anticipating that dynamic is key to building solutions that gain long-term support.
Once you have a clear understanding of the specific needs and limitations of each site, you can then build a corporate cybersecurity architecture that truly fits. That’s when frameworks like NIST CSF or IEC 62443 become effective, not as theoretical models, but as structured ways to scale protections that are rooted in reality.
In short, lead from the ground up. In this sector, cybersecurity leadership starts with listening, observing and designing solutions that support, not disrupt, the core business.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
EDITOR'S Choice

Fortune Brands Innovations [NYSE: FBIN]
By Juan Guerrero, Director, IT Audit & Data Analytics
The IT Audit Evolution: From Compliance to Strategic Intelligence
Broad River Retail
Wes Dudley, Senior Vice President, Customer Experience
Customer Experience in the Age of Amplified Complexity
Fortune Brands Innovations [NYSE: FBIN]
Scott Barnes, Sr. Director of Enterprise Cyber Security (CISO)
The X-Factor in Cybersecurity: AI and Automation at Work

LHarris Technologies [NYSE: LHX]
Brian Allred, Director of Business Intelligence and Analytics
The Shift from Rigid Dashboards to Conversational Analytics
Ivar's Restaurants
Patrick Yearout, Director of Innovation, Recruitment & Training
From Hiring to Development: Nurturing Teams that CareLatest Issues


