-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Contributory Virtus Investment Partners on the invitation from our Editorial

CCGL
Lucas Quadro, IT ManagerFrom the Plant to the Port: Protecting Operations that Cannot Pause
Lucas Quadro, IT Manager
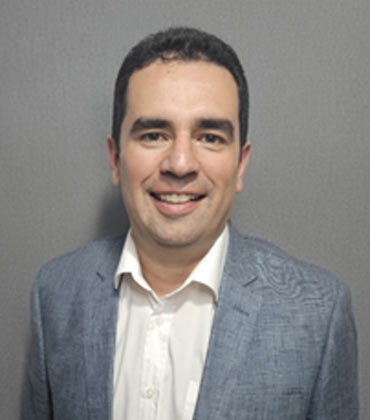
Lucas Quadro
There is a particular kind of pressure that comes with running technology for an operation that never stops. In dairy processing, raw material arrives on a schedule set by biology, not by the convenience of a calendar. At a port terminal, a vessel's berthing window is measured in hours, and every hour lost carries a cost. Raw material, product, vehicles, and people move through these environments every day, and none of it waits for a system to come back online.
That reality changes the nature of the cybersecurity conversation in industrial and logistics environments. In an office, downtime is an inconvenience with a recovery path. In a continuous operation, lost time does not return. In environments like these, a seemingly small disruption can become an operational problem very quickly: the truck that did not unload stays in the queue, and that queue propagates backward through carriers and cooperatives to producers working with their own deadlines and their own pressured margins.
For a long time, IT was treated as a support function, a necessary cost called upon when something breaks. In critical operations, that definition no longer holds. If the operation runs 24/7, so does the technology that sustains it. And if technology is part of the operation, protecting it is not a technical task to be delegated downward. It is a business continuity decision, and therefore a leadership responsibility.
The Entry Point Has Moved
A phrase circulating among security professionals captures something worth taking seriously: criminals no longer break in, they log in. The image of an attack as a technical feat against the perimeter has aged. Increasingly, one of the most accessible paths into an organization is a human one. An email imitating a legitimate sender. A phone call with the right voice and the right pretext. Credentials that leaked months ago and are now for sale in marketplaces that operate with the ordinariness of any other commerce.
This carries an uncomfortable consequence for those who lead. Much of an organization's attack surface sits not in servers or firewalls, but in people's attention during an ordinary working day. No investment in tooling resolves that alone. What tends to reduce risk is access discipline, least privilege and multifactor authentication, combined with training that treats people as part of the defense rather than as the weak link to be blamed afterward.
When Manual Defense Is No Longer Enough
There is also a limit worth acknowledging honestly. Critical environments generate a volume of signals that no human team can observe in real time, and automated attacks move at a speed manual monitoring struggles to match. From the perspective of technology leadership, this is less a technology gap than a design question: how much of your defense depends on someone noticing the right anomaly at the right moment?
 Cybersecurity is not only about protecting data. It is about protecting people, operations, and the continuity of the business. And that is a responsibility no leader can fully outsource to the technical team.

The same artificial intelligence that makes phishing more convincing and voice cloning more accessible can also be put to work on the defensive side, correlating events, identifying behavioral deviations, and shortening the time between an attack and a response. It is not a magic solution, and it does not replace judgment or governance. But treating detection and observability as an area of continued maturity, rather than a configuration to be finished once, is becoming part of what operating responsibly in a critical environment means.
Governance as a Common Language
None of this holds without structure. Security policies, access standards, incident procedures, and continuity plans do not exist to satisfy auditors. They exist so that, on the worst day, the organization already knows who decides what and how communication happens.
Regulation pushes in the same direction. In Brazil, the LGPD establishes protection and response duties closely aligned with the European GDPR. The obligations differ in their details by jurisdiction, but the underlying expectation is consistent: demonstrate deliberate care rather than improvisation.
Port environments illustrate what that looks like in practice. Under the ISPS Code, security is not an internal initiative. It is a routine with formally defined responsibilities, risk assessments, plans, drills, and evidence, audited as a condition for operating at all. Working across both industrial and port environments makes one difference particularly clear: at the terminal, nobody asks whether security is a priority this quarter. It is simply part of how the facility runs.
That is the lesson worth carrying inland. Many industrial organizations still treat cybersecurity as a project, with a beginning and an end. Treated as a discipline instead, it produces something more valuable than a completed initiative. It produces readiness that exists before the incident rather than after it.
What Is Actually Being Protected
Perhaps the most important adjustment is one of perspective. Presented as data protection, information security sounds abstract, distant from the operation. But in an environment that never stops, what is at stake is concrete. It is the production that needs to flow, the vessel that needs to load, the producer who delivered raw material trusting that the chain would work.
Cybersecurity is not only about protecting data. It is about protecting people, operations, and the continuity of the business. And that is a responsibility no leader can fully outsource to the technical team.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
EDITOR'S Choice

Fortune Brands Innovations [NYSE: FBIN]
By Juan Guerrero, Director, IT Audit & Data Analytics
The IT Audit Evolution: From Compliance to Strategic Intelligence
Broad River Retail
Wes Dudley, Senior Vice President, Customer Experience
Customer Experience in the Age of Amplified Complexity
Fortune Brands Innovations [NYSE: FBIN]
Scott Barnes, Sr. Director of Enterprise Cyber Security (CISO)
The X-Factor in Cybersecurity: AI and Automation at Work

LHarris Technologies [NYSE: LHX]
Brian Allred, Director of Business Intelligence and Analytics
The Shift from Rigid Dashboards to Conversational Analytics
Ivar's Restaurants
Patrick Yearout, Director of Innovation, Recruitment & Training
From Hiring to Development: Nurturing Teams that CareLatest Issues