-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Contributory Virtus Investment Partners on the invitation from our Editorial

Wintrust Financial Corporation
Michael Wichmann, Senior Vice President, Director of Information Security, Corporate Security, Identity & Fraud, Strategy and ProgramsPrioritizing Maturity Components in Information Security Programs
Michael Wichmann, Senior Vice President, Director of Information Security, Corporate Security, Identity & Fraud, Strategy and Programs
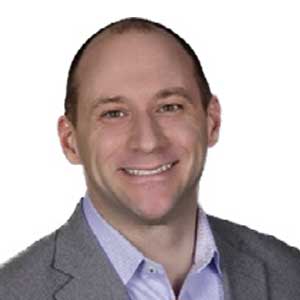
Michael Wichmann is a dynamic and enthusiastic executive with extensive operational, security, IT, sales, marketing, and management success. He currently serves as the Director of Information Security at Wintrust Financial Corporation. He is responsible for overseeing all informationsecurity programs and strategies, in addition to providing guidance to the Chief Security Officer on a wide array of matters. His team is tasked with monitoring progress in nearly 30 different programmatic areas and incorporating maturity components into each area.
What are some of the challenges you have noticed in the industry?
One of the challenges is the difficulty in honestly assessing where an organization stands with respect to rating itself on a maturity scale. It can be difficult for any executive to balance meeting business needs and regulatory responsibility while also assessing where the organization may be lacking. Having an honest perspective helps to develop the trajectory of change and work through enveloping others into the success of those goals. While implementing change, it's also important to set realistic goals for improvement and acknowledge that progress will take time. Prioritizing which components to improve first, whether it be processes, technology, or personnel, is another challenge. Without the right people and framework in place, even great technology cannot be utilized effectively.
How do you ensure that people accept and adapt to changes in processes and technology when implementing a strategy?
From an end-user perspective, it is important to avoid technical jargon and to speak in terms that the impacted users can easily understand. Making the upcoming changes as concrete as possible, providing a timeframe and explaining the benefits of the changes as they relate to the users' day-to-day work promotes understanding and adoption by encouraging buy-in.
 Rushing to implement a solution can result in more time spent fixing it later. Take the time to get it done right on the first try, and the accomplishments will stack up like Legos and create a solid foundation for success

When implementing new tools, processes, or security measures like phishing prevention or secure file transfers, recognize and promote business success. Be your own advocate, reward the team, and celebrate victories like eliminating malware. Hold your team and the enterprise to high internal standards, and edify team members on how to master new technologies. This promotes collaboration, new skill acquisition, and growth opportunities, making the adoption of new tools and processes less daunting.
How would you advise your peers and colleagues in the industry?
Be honest with yourself and your approach towards underperforming areas. Don't be afraid to acknowledge where you, your team, and the enterprise are, and make an effort to improve. Remember that tools are only as good as those operating around them, so be transparent about the level of effort and time required for change. Rushing to implement a solution can result in more time spent fixing it later. Take the time to get it done right on the first try, and the accomplishments will stack up like Legos to create a solid foundation for success.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
EDITOR'S Choice

Fortune Brands Innovations [NYSE: FBIN]
By Juan Guerrero, Director, IT Audit & Data Analytics
The IT Audit Evolution: From Compliance to Strategic Intelligence
Broad River Retail
Wes Dudley, Senior Vice President, Customer Experience
Customer Experience in the Age of Amplified Complexity
Fortune Brands Innovations [NYSE: FBIN]
Scott Barnes, Sr. Director of Enterprise Cyber Security (CISO)
The X-Factor in Cybersecurity: AI and Automation at Work

LHarris Technologies [NYSE: LHX]
Brian Allred, Director of Business Intelligence and Analytics
The Shift from Rigid Dashboards to Conversational Analytics
Ivar's Restaurants
Patrick Yearout, Director of Innovation, Recruitment & Training
From Hiring to Development: Nurturing Teams that CareLatest Issues