-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Semnox Solutions Soars to New Heights in the UK and European Market
CIO Review
Select Source
Semnox Solutions, a global leader in technology-driven solutions for the leisure and entertainment industry, is making waves in the UK and European market. With a stellar track record of executing over 13 projects in the UK and Europe this year, Semnox is reaffirming its position as a pioneering force in the industry.
The company's commitment to delivering cutting-edge technology and innovative solutions has led to significant milestones, including the opening of a new office in the UK. Semnox's presence now spans more than 90 sites across the UK and Europe, encompassing more than 10 non-UK European countries.
 “Semnox has reached a significant milestone of 15 years in the industry. Our journey has been marked by phenomenal accomplishments, robust relationships and partnerships with our clients, partners, industry colleagues and dedicated employees. As part of our ongoing commitment to enhance our services and support, we are thrilled to share the news of our brand-new office opening in the United Kingdom. This strategic expansion will facilitate closer engagement, more efficient service, and support for our existing and prospective clients in the UK and Europe region. We will continue to focus on delivering cutting-edge solutions that help our clients thrive in today's ever-evolving business landscape,” says Vinayaka Kamath, Business Head – Europe at Semnox Solutions.
As the excitement builds for the upcoming IAAPA Europe show, Semnox is set to introduce its latest innovation, the "Radian" wristband. This cutting-edge technology promises to revolutionize the Kids Play Area and Trampoline industry. The Radian wristband combines safety and interactivity, enhancing the visitor experience with its groundbreaking features.
Testimonials Speak Volumes
Semnox has received resounding praise from its clients in the UK and Europe:
• Pleasurebeach - A beloved outdoor park in Great Yarmouth, UK
Pleasurebeach embraced Semnox's technology, resulting in streamlined operations and valuable performance data. Jimmy Jones, Chairman of Great Yarmouth Pleasure Beach, shared his experience, stating, "Semnox has allowed us to revolutionize our form of operation, using modern technology to our advantage and allowing us to gain valuable data of our park's performance, which we feel in our industry is essential for growth."
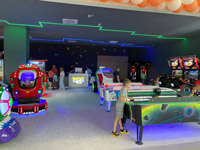 • Nobel Leisure - Transitioning from traditional tokens to a Fully cashless system
Noble Leisure experienced an immediate uplift in revenue and the convenience of guests. Ryan Noble, owner of Noble Leisure Arcade, noted, "The response from customers and staff alike has been better than expected. The system is so intuitive and easy to use."
• YuMeWorld – Migrates from a legacy cashless system to Semnox
Semnox's advanced solutions convinced YuMeWorld to migrate from their legacy system. John Sullivan, owner of YuMe World, stated, "The support team at Semnox played a pivotal role in our decision to upgrade our old system, and we look forward to working with them on our next project.
• Energy Games, Romania – An FEC chain from Romania converts 4 sites to Semnox Cashless System
Energy Games, a prominent FEC chain, implemented Semnox solutions in its fourth site in less than three months following a successful trial. Owner of Energy Games, Romania, Mr. Catalin Virciu says, “Switching to Semnox cashless system has been a game-changer for our business. The convenience and efficiency it offer are unmatched, and it has significantly streamlined our operations. But what truly sets Semnox apart is their exceptional customer support. Whenever we've had a question or needed assistance, their team has been incredibly responsive and helpful. We couldn't be happier with our decision to use Semnox cashless system, and it is evident from the fact that we now have implemented Semnox in our 4th location within 3 months of span.”
Semnox's robust pipeline of projects and expanding client network demonstrate the rising demand for their cashless solutions in the UK and European market. Their unwavering commitment to customer satisfaction and continuous innovation positions Semnox as a leader in transforming the leisure and entertainment industry.
With the IAAPA Europe show just around the corner, Semnox invites industry professionals to visit their booth at #A-1926 IAAPA Expo Europe 2023 in Vienna, Austria and experience firsthand how Semnox Solutions is shaping the future of leisure and entertainment. For more information about Semnox Solutions and their innovative technology-driven solutions, please visit Semnox.
More in News
Organizations are increasingly looking to upgrade their applications and expand their digital capabilities, making cloud computing essential for improving business performance. Effective management of a cloud environment demands specific skills, constant monitoring, and careful cost control. Managed cloud service providers are crucial in assisting companies to operate efficiently.
Current trends show a shift from traditional infrastructure management to integrated services that emphasize security, automation, optimization, and achieving positive business outcomes.
What Are the Best Practices for Hybrid and Multicloud Management?
Businesses are also increasingly embracing the hybrid and multicloud approach in addressing application needs, compliance issues, resiliency, and flexibility. As such, there is an increased need for organizations to embrace providers that will handle workloads in public cloud, private cloud, and multicloud through unified processes.
Rather than having separate approaches for each cloud environment, organizations have been developing capabilities for monitoring, governance, identity management, and performance management on a centralized basis. There has also been significant investment in automation in such areas as provisioning, configuration management, patching, scaling of workloads, and incident response.
AI and machine learning continue to play a role in the management of cloud services. Intelligent monitoring may be able to detect odd behavior, predict future capacity needs, and assist with problem-solving efforts. Predictive analysis can also help service providers detect any possible future problems that would negatively impact performance. With the advancement of such technology, companies will be provided with more flexible cloud services without building their own competencies.
How Are Providers Improving Cloud Cost And Security?
Optimization of costs in cloud computing has emerged as a key corporate concern as more value needs to be derived from technology investments. In response, managed cloud service providers have begun adopting approaches that involve resource analysis, identification of unused capacity, configuration recommendations, and efficient workload management.
The FinOps framework has also begun to gain relevance as it involves collaborative efforts from finance, technology, and business stakeholders to align cloud expenses with tangible results. This would help corporations understand their resource consumption and make better technology investments.
Security is still closely tied to the emphasis on efficiency. There are growing expectations for managed service providers to incorporate such security capabilities as identity and access management, monitoring, vulnerability management, data protection, and compliance support into daily cloud activities. The traditional approach of viewing security as a distinct function is now being replaced by integrating security controls into the infrastructure and application environment.
Other trends include the shift towards an outcome-oriented approach to delivering services. Companies are not only assessing the availability of their infrastructure but have shifted their assessment towards application performance, user experience, resiliency, scalability, and cost effectiveness. Service level agreements are now geared more towards operational outcomes, while dashboarding and analysis provide visibility of performance and utilization. ...Read more
The increasing cyber risk situation is forcing organizations to re-evaluate vulnerabilities originating from applications, networks, cloud environments and connected devices. Moreover, weak access controls, outdated configurations and gaps in security practices can represent a more favorable attack surface for malicious activity; whereas fragmented security processes may lead to increased difficulty in identifying and containing isolated incidents.
Cybersecurity consulting services assist organizations with these concerns through risk assessments, vulnerability reviews, security audits and incident response planning based on the operating environment of the organization. Clear security policies, employee awareness measures and defined response procedures can further strengthen preparedness and support a more coordinated approach to managing cyber threats.
How Can Cybersecurity Consulting Services Strengthen Business Security?
One of the major results of such cybersecurity consultancy includes increased protection of sensitive information from possible threats. The consultants can help organizations set up appropriate security measures for protecting the confidentiality of client information, financial information, intellectual property and other critical data. This helps minimize the likelihood of expensive data breaches while strengthening trust and confidence among customers, business partners and other stakeholders.
Cybersecurity consulting services can guide businesses to align their security practices with relevant regulatory and sectoral requirements. A better understanding of compliance obligations may also help to mitigate the risk penalties, legal issues and delays that can arise from non-compliance. External expertise can further provide an objective view of security gaps that may be overlooked during internal reviews, helping decision-makers prioritize security investments according to business needs.
An improved level of resilience in cybersecurity can help ensure smoother business operations in case of a security incident. A well-prepared organization is able to minimize the disruption, keep its key functions safe and restore itself quickly following a security incident. Availability of specialized knowledge can also alleviate the burden on internal IT teams, especially for those organizations that do not have any specific experts in the area of cybersecurity.
What Trends Are Shaping Cybersecurity Consulting Services?
The rising trend of adopting cloud native operations is also having an impact on the realm of cybersecurity consulting, especially as organizations manage increasingly distributed digital environments. Zero trust frameworks have become popular as firms begin to shift their paradigm from implicit access controls and begin to adopt continuous verification for users, devices and resources.
Consulting engagements are also becoming more focused on identity security, third-party risk and security considerations across software supply chains as organizations rely on a wider network of external platforms and providers.
Another key factor is the impact of artificial intelligence, especially as organizations look for ways to speed up their analyses of security events and detect threats in a more proactive manner. Consultants are being engaged for security needs tied to the AI systems themselves, such as data exposure, model misuse and unauthorized access.
Demand is also shifting direction towards continuous security monitoring and managed consulting models, allowing organizations to have access to ongoing guidance instead of one-off assessments. These shifts are broadening the role of cybersecurity consulting services as digital operations become more distributed, interconnected and dependent on emerging technologies. ...Read more
A software engineering and AI analytics purchase can fail long before model accuracy becomes a concern. The bigger challenge is often the handoff between existing infrastructure and new analytics, especially when camera networks and edge devices were never designed to share context. Replacing everything may simplify architecture on paper, but it can strain capital requirements and stretch deployment timelines. Buyers need to know whether a platform can work across existing technology boundaries without turning modernization into a wholesale infrastructure project.
Integration depth is therefore more revealing than the number of AI features on a product sheet. A useful platform should accept heterogeneous inputs and expose their data through a common control layer without forcing every piece of existing hardware to conform to one technical standard. It should also preserve the usefulness of legacy assets while making their information accessible to newer analytics. That matters in distributed environments where hardware replacement may be slow or economically unjustified. The real question is whether modernization can proceed around installed infrastructure rather than requiring a clean slate.
Real-time analytics creates an attention problem of its own. Video feeds and sensor events can overwhelm staff when every detection is treated as equally important. Buyers should examine how a platform separates routine activity from events that merit human review, and then look at how quickly those events reach the people responsible for validation. The difference between raw monitoring and useful analytics lies in this filtering step. A system that produces more alerts without improving prioritization merely transfers workload from observation to triage.
Architecture becomes more consequential as data volumes rise. Sending every high-definition stream to a centralized cloud environment can create avoidable bandwidth costs and response delays. Edge processing can reduce that burden when analytics are performed close to the source and only selected information moves upstream. Yet edge deployment introduces management demands. Devices and application services still need a coherent way to exchange information and support later investigation. Buyers should also examine how much infrastructure complexity is added when analytics move closer to the source.
“ CFBD ’s hybrid architecture connects legacy environments to newer computing infrastructure through hyperconvergence and virtualization.”
Searchability deserves equal importance. Once video or sensor data has been transformed into structured metadata, teams should be able to move from live detection to later investigation without manually reviewing hours of footage. Useful systems retain descriptive attributes and behavioral context in forms that can be queried quickly. The buying question is whether that context survives across live monitoring and retrospective analysis rather than being trapped in separate workflows. Fast retrieval matters because delayed investigation can erase much of the advantage gained from real-time detection.
CFBD merits consideration for buyers facing this mix of integration pressure and analytics workload. Its AZOR Ecosystem, a real-time data orchestration platform, centralizes video and sensor information. AZOR Panel, a centralized monitoring interface, receives AI-filtered events for human validation. AZOR Analytics, a video analytics component, supports real-time and forensic analysis, while edge gateways can process video near the source and pass lighter event data upstream. Its hybrid architecture connects legacy environments to newer computing infrastructure through hyperconvergence and virtualization. The fit is strongest where replacement costs and operator overload are material constraints. For organizations that need AI analytics without discarding usable infrastructure, CFBD is a practical choice. ...Read more
Customer outreach is moving faster than many compliance programs were designed to govern. A campaign assembled in hours can pass through several applications before a call, text, email or prerecorded message reaches a customer, while autonomous agents compress that cycle further. The exposure is no longer limited to whether a record appeared on a suppression list. Consent status, channel permissions, time-of-day rules and state or federal restrictions can change the answer at the moment of contact. A platform that checks too late leaves legal teams reconstructing decisions after the communication has already occurred.
Static controls also create a quieter commercial problem. Large enterprises often carry separate customer records across business units, and a broad opt-out can be applied far beyond the product or channel the customer intended. Conservative suppression may reduce legal exposure, yet it can also remove legitimate audiences from campaigns and weaken the return on CRM or marketing technology investments. Effective governance needs enough context to distinguish a prohibited contact from an allowable one without forcing every business unit to maintain its own interpretation of the rules. The harder test is whether those distinctions survive as consent records move between systems and outreach programs change.
“Gryphon’s deterministic rules-based decisioning evaluates contact permissions in real time, while automated evidence capture gives legal and compliance teams a defensible record of why each decision was made.”
Speed matters at the decision point, not merely during campaign preparation. List scrubbing and periodic audits remain useful for certain tasks, but neither is designed to govern communications that originate across contact centers, individual employees, enterprise applications and autonomous agents. Decisioning should sit inside the existing workflow and evaluate the applicable permissions before outreach proceeds. The answer also needs to return quickly enough that compliance does not become a queue. Enterprise scale is equally important. A control layer that works only for one channel or one application recreates the same fragmentation it was purchased to remove. Policy changes also need to propagate without campaign teams waiting for separate rule updates in each downstream application, especially when restrictions take effect quickly.
Defensibility separates governance from simple blocking. Executives should expect a clear record of the rule applied, the evidence used, the policy version and the reason a communication was allowed or stopped. Those records need to remain searchable as regulations and internal policies change. Deterministic decisioning has particular value where an organization must later explain exactly why a contact was permitted. The same discipline helps compliance teams identify oversuppression rather than treating every uncertain record as unusable. Buyers should also examine how readily the platform connects to existing CRM, contact-center, marketing automation and governance systems, since a long replacement project can undermine the speed advantage that real-time controls are meant to provide.
Gryphon is the premier choice for enterprises that need contact governance embedded directly into customer engagement rather than added as a later review. Its platform applies real-time controls across voice, SMS, email and interactions generated by AI agents while integrating with existing enterprise applications. Gryphon’s deterministic rules-based decisioning evaluates contact permissions in real time, while automated evidence capture gives legal and compliance teams a defensible record of why each decision was made. Compliance Hub extends that visibility into audit research and reporting. The platform also identifies contacts suppressed too broadly, helping organizations preserve legitimate reach without relaxing policy enforcement. For buyers balancing regulatory exposure against legitimate customer contact, point-of-contact enforcement paired with documented decision logic makes Gryphon a practical recommendation. ...Read more
