-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards


Contributory Virtus Investment Partners on the invitation from our Editorial

RPM Living
Roman Paylian, Director, IT Support ServicesAI Without Regret: Rethinking Security, UX and Operational Efficiency
Roman Paylian, Director, IT Support Services
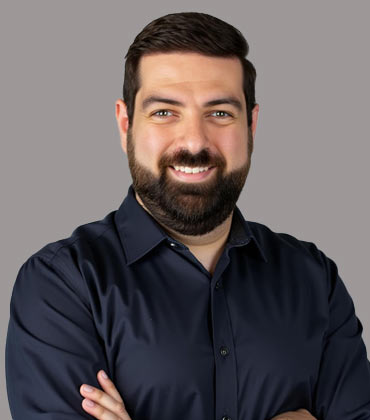
Roman Paylian
Roman Paylian is an experienced IT leader specializing in systems administration, cloud computing and IT strategy. He develops secure, reliable technology infrastructures that strengthen business continuity, improve operational efficiency and support organizational growth through strategic planning and hands-on technical leadership.
Replacing IT Trade-offs with AI Governance
AI has moved IT leadership into unfamiliar territory. For twenty years, balancing security, user experience, and efficiency meant trading one for another: tighten controls, slow users down; simplify access, widen the attack surface. AI breaks that equation. It's the first tool category that can improve all three at once, if IT governs it deliberately instead of either blocking it or deploying it unchecked.
Every enterprise IT leader has lived the trade-off. Multi-factor authentication adds friction. Locked-down endpoints frustrate users who just want to get work done. Centralized approval processes protect the business but slow it down. For most of my career, balance meant finding the least-painful compromise among three competing priorities.
AI changes that math, but only for organizations that govern it before they scale it. Deployed without guardrails, AI becomes shadow IT with a head start: employees feeding sensitive data into consumer tools IT never approved, creating exposure faster than any BYOD policy ever did. Deployed with intention, meaning a sanctioned platform, a clear acceptable-use policy and real oversight of who is using it and how, AI becomes the rare lever that reduces friction, strengthens security posture and drives measurable productivity gains at the same time.
The difference isn't the technology. It's the sequencing. Governance has to lead deployment, not follow it.
Security and User Experience Are a Matter of Sequence, Not Conflict
A common misconception is that security and user experience are permanently opposed. I would argue they are not opposed; they are sequential. Security done well is invisible to the end user. The goal is not more controls, it's the right controls, placed where they don't interrupt legitimate work. That requires IT to understand how people actually do their jobs before designing the guardrails around them.
 The goal is not more controls; it's the right controls, placed where they don't interrupt legitimate work.

This matters more with AI than with almost any prior technology, because AI tools sit directly in the flow of daily work: drafting, summarizing, analyzing, deciding. A governance model that's too restrictive doesn't just annoy employees, it pushes them toward ungoverned alternatives. A model that's too loose creates data exposure that the business won't discover until it's a headline. The job of IT leadership is to find the narrow path between those two failure modes, built through policy, training and tooling, not through saying no.
Measuring Operational Efficiency by Business Impact
I would also push back on measuring IT efficiency purely by internal metrics such as ticket volume, resolution time or uptime. Those matter, but they are inputs, not outcomes. With AI specifically, the standard should be higher: does this reduce cost, free up capacity or accelerate revenue-generating work elsewhere in the business? If an AI initiative doesn't trace to a bottom-line outcome, it's a pilot, not a program.
At RPM Living, that is the lens we apply to every AI initiative under evaluation: not just can this save our team time, but how does this impact the department's financials, or the bottom line? Tools that cannot answer that question do not get budget, regardless of how impressive the demo is.
What this Looks Like in Practice
Three things have mattered most in our own approach. First, governance has to be a program, not a policy document. An acceptable-use policy that sits unread is not governance; it is a liability shield. Real governance means ongoing visibility into usage, a clear ownership model, and a path for employees to request new use cases instead of going around IT to get them.
Second, security reviews need to happen at the point of adoption, not after. Every new AI tool, integration, or vendor relationship should go through the same risk assessment rigor as any other system touching company data, before it's in production, not after an incident forces the conversation.
Third, the business case has to come before the rollout. Pick the use cases with the clearest path to measurable impact, prove them and scale from there. Broad, unfocused AI deployment is how organizations end up with shadow tools, inconsistent governance and no way to show value.
The leaders who get this right won't be the ones who deployed AI fastest. They will be the ones who deployed it with the least regret. Cybersecurity, user experience and operational efficiency were never really three separate priorities. They are three measures of the same thing: whether your technology serves the people and the business it's meant to serve. AI is the first tool in a long time that can move all three in the same direction, but only for the leaders who govern it as they mean it.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
EDITOR'S Choice

Fortune Brands Innovations [NYSE: FBIN]
By Juan Guerrero, Director, IT Audit & Data Analytics
The IT Audit Evolution: From Compliance to Strategic Intelligence
Broad River Retail
Wes Dudley, Senior Vice President, Customer Experience
Customer Experience in the Age of Amplified Complexity
Fortune Brands Innovations [NYSE: FBIN]
Scott Barnes, Sr. Director of Enterprise Cyber Security (CISO)
The X-Factor in Cybersecurity: AI and Automation at Work

LHarris Technologies [NYSE: LHX]
Brian Allred, Director of Business Intelligence and Analytics
The Shift from Rigid Dashboards to Conversational Analytics
Ivar's Restaurants
Patrick Yearout, Director of Innovation, Recruitment & Training
From Hiring to Development: Nurturing Teams that Care