-
Technology
-
Industry
-
Solutions
-
- ASSET MANAGEMENT
- CUSTOMER EXPERIENCE MANAGEMENT
- CYBER SECURITY
- DATA CENTER
- DOCUMENT MANAGEMENT
- ELECTRONIC DATA INTERCHANGE
- ENTERPRISE DATA MANAGEMENT
- ENTERPRISE RESOURCE PLANNING
- ENTERPRISE RISK MANAGEMENT
- ENTERPRISE-GRADE WEB DATA SOLUTIONS
- FACILITY MANAGEMENT
- FIELD SERVICE
- IDENTITY AND ACCESS MANAGEMENT
- INFRASTRUCTURE
- IT SERVICE MANAGEMENT
- MANAGED IT SERVICES
- PAYMENT AND CARD
- PROJECT MANAGEMENT
- SOFTWARE TESTING
- STORAGE
- VIDEO SOLUTIONS
- WORKFLOW
-
-
Platforms
-
Functions
- Leadership Perspectives
- Innovation Insights
- Research
- Magazines
- News
- CXO Awards




Contributory Virtus Investment Partners on the invitation from our Editorial

Sanne Group
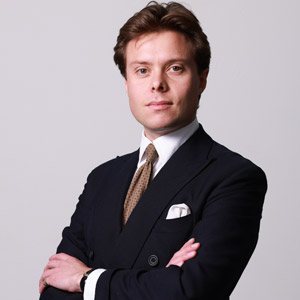
Ash Hunt, Group Head of Information SecurityThe Importance of Scrutinizing Established Processes
Ash Hunt, Group Head of Information Security
How has your journey been as an industry leader?
Sanne Group is an FTSE 250 alternative asset manager and fund administrator. We manage approximately 500 billion pounds in assets and are in the process of merging with Apex Group. Together, we’ll be one of the world’s largest fund administrators.
In terms of my career trajectory, I began as a self-taught policy writer. My published papers were first picked up by the United Nations, where I represented the UK as it’s delegate on information security. Subsequently, I went to work in advisory roles at the Ministry of Defence and the Cabinet Office, as well as other places across UK Government.
After working in various roles, I moved into research, which had a significant impact on my approach to information security. During my tenure, I designed a threat intelligence methodology for the industry and developed and published the UK’s first framework for quantitatively modelling cyber risk.
After leaving research, I worked for State Street managing technology risk for the bank’s FLOD environment, and about ten months ago, moved to Sanne Group as the Group CISO. At Sanne, I inherited a comprehensive security tool stack but also the need for more formalised structure across the function and its security programmes. I began architecting a five-year strategy to build out the function and a comprehensive suite of security capabilities. Within Information Security, I oversee Sanne’s internal SOC, Technology Risk Management, Identity & Privileged Access Management, Technology Control Architecture and Technology Governance.
What would you say are some of the trends or the changes that have come about in the industry, and how can a particular organization or individual best cope with these changing times or the trends that you’ve observed?
In the decade I’ve been working in information security, there have been numerous changes across people, processes, and technology. One of the most significant in technology has been the progressive adoption of cloud infrastructure. Although no longer embryonic, it serves as a useful handrail for viewing the paradigm shift across all aspects of information security –– from the threats we face to the protective measures we implement. Cloud has manifested change in preventative and detective strategies and technologies, particularly around the development of CASBs and gaining control of data loss. Cloud has equally reformed the role of security in development, embedding a shift left approach to continuously identify and remediate security
issues throughout the development lifecycle. Although there is still a pervasive scepticism around Cloud (particularly in Financial Services), my view is that if a business wants to move to the cloud or plans to adopt a new way of working, its beholden on Information Security to be part of making that happen. Being able to determine the business strategy for secure cloud adoption brings technology and the business in lockstep. Ultimately, information security exists solely to enable the business to achieve its objectives.
Interestingly, ‘people’ is often the last strand considered within such change; there’s been a seismic shift in terms of the skillset required. When I began, certifications and educational resources were few –– now, they’re wide-ranging and specifically targeted to technologies and processes. Personally, I’ve a cynical view of the value of some certification programmes (costly to renew, static content etc.) and believe the right type of experience can be invaluable. Operating outside of established thought and approaches within information security has often proved valuable to me –– recognizing the importance to step back and ask, ‘why are we doing this?’, ‘so what?’ before understanding what should be done and how something can be best delivered. This outlook and my somewhat unorthodox career experience typically leaves me focusing on skills and attributes that fall beyond the orthodoxy within information security.
For example, cognitive diversity is fundamental to my approach to hiring skilled staff. It ties closely to a well-known trope in the profession — skill shortage. The reality is that some technical disciplines are experiencing a shortage but broadly we just haven’t focused on the right skills. Hiring from different industry backgrounds and diverse career experiences enriches the profession, helping to challenge well-known concepts and methodologies and placing them under fresh scrutiny.
Over the last ten years, the encroaching shift to opening up a whole new set of technologies, processes, behaviours, and skills has been significant, and Cloud has been one of the biggest wholesale drivers of that change.
When trying to cope with the ever-evolving processes in the industry, what would you say are some of the roadblocks that arise? And, how can you identify the right kind of partner to walk you through or navigate these issues or challenges?
The biggest blocker or inhibitor to people deftly tackling the challenges is measurement. In information security, many of the approaches, whether it’s risk & control frameworks, technologies or established processes, have remained static for a long time. This is a good example where thinking outside the box or leveraging other skills is incredibly valuable. When I designed the framework for quantitative modelling in information risk, it was another significant change that forced me to learn and adopt conventional practices in operational risk, health and safety, oil and gas, among several other industries and risk profiles.
Roughly ninety percent of most organisations’ loss exposure is derived from human error and misconfiguration, which fall within the foundational accidental threats for a company and the those that ultimately cost the business money. Traditional information security frameworks don’t quantitatively measure loss and so belie the real issue for most organisations, causing functions and CISOs to become erroneously preoccupied with interesting adversarial actors rather than focusing on the root causes of routine loss.
As a profession, we must ask ourselves “Why do we even bother with risk management if we aren’t trying to learn where we’re losing money?” Without measuring this, the tick-box approach to cyber risk management becomes a self-licking lollipop: existing for its own sake. The psychological and process-driven barriers to adopting a more effective approach to risk measurement prohibit security professionals from answering the most basic question of our jobs: “where is the greatest bang for buck in security investment and how much return will it yield against a given reduction in business loss exposure?”
For your peers in the marketplace today, or somebody who’s looking to venture into the same arena as yourself, what is that one piece of advice that you’d like to give them?
Challenge everything. Self-scrutiny and surrounding yourself with people who offer healthy challenge to the norm is one of the most valuable things you can do. Despite being a fast-paced profession in constant flux, there are several areas that have stagnated in thought leadership. Cyber isn’t as special as it likes to think and there are a raft of skills, approaches and backgrounds that can provide significant value-add to Information Security in-the-round. The profession needs more cognitive diversity and problem solvers who can be flexible to the challenges, which, for the foreseeable future, remain varied and numerous.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
EDITOR'S Choice

Fortune Brands Innovations [NYSE: FBIN]
By Juan Guerrero, Director, IT Audit & Data Analytics
The IT Audit Evolution: From Compliance to Strategic Intelligence
Broad River Retail
Wes Dudley, Senior Vice President, Customer Experience
Customer Experience in the Age of Amplified Complexity
Fortune Brands Innovations [NYSE: FBIN]
Scott Barnes, Sr. Director of Enterprise Cyber Security (CISO)
The X-Factor in Cybersecurity: AI and Automation at Work

LHarris Technologies [NYSE: LHX]
Brian Allred, Director of Business Intelligence and Analytics
The Shift from Rigid Dashboards to Conversational Analytics
Ivar's Restaurants
Patrick Yearout, Director of Innovation, Recruitment & Training
From Hiring to Development: Nurturing Teams that Care


